

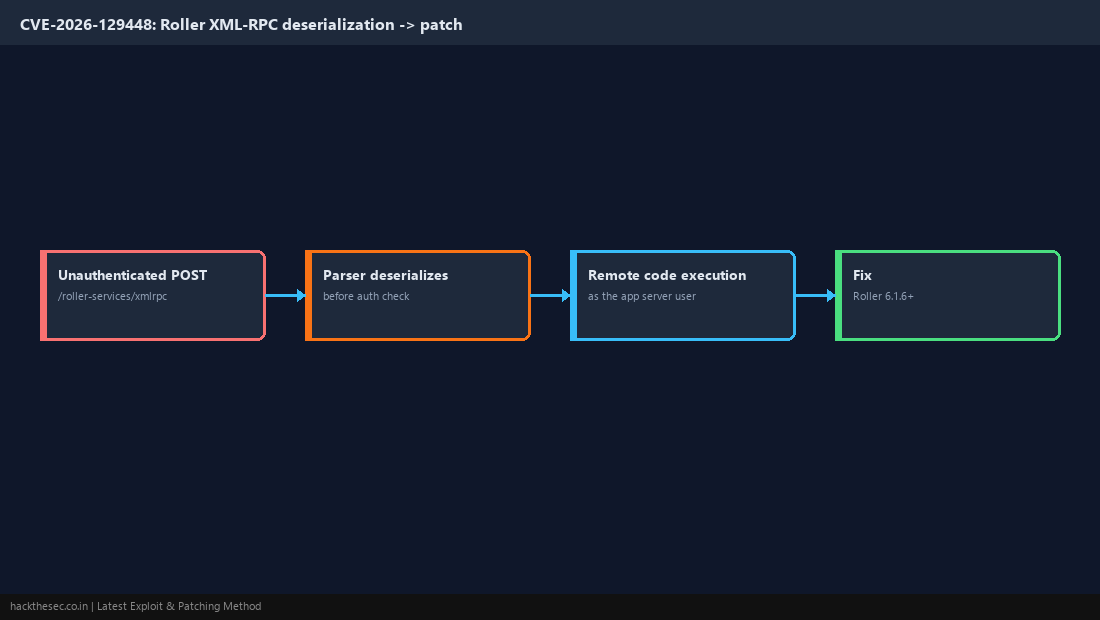
⚠ HIGH PRIORITY — actively exploited, added to CISA KEV on Nov 20, 2026 (federal due date Nov 23, 2026). CVE-2026-129448 is an unauthenticated remote code execution flaw in Apache Roller, the Java blog server. The XML-RPC endpoint deserializes vendor extension types before it checks who is calling. CVSS 9.8 Critical.
This is the same bug as CVE-2026-82384 (Sept 2026), which originally listed only Roller 6.1.5. The new CVE widens the affected range all the way back to Roller 4.0.0, so many sites that thought they were unaffected are not.
Affected and fixed versions
- Affected: Apache Roller 4.0.0 through 6.1.5
- Fixed: Apache Roller 6.1.6 or later
- No special configuration needed to be vulnerable: the servlet is mapped even when XML-RPC is turned off in the admin UI
Patching Method
- Back up the Roller database and your current
roller.war/ exploded webapp androller-custom.properties. - Download Roller 6.1.6 from the Apache Roller project and deploy it to your servlet container (Tomcat, Jetty, etc.).
- Restore
roller-custom.properties, restart the container, and confirm the new version in the admin pages.
Workaround if you cannot upgrade today
The Apache record gives two options. Disabling XML-RPC in the Roller admin UI is not enough.
- Set
enabledForExtensionstofalseinWEB-INF/web.xml, or - Remove the
/roller-services/xmlrpcservlet mapping fromWEB-INF/web.xml, - then restart Roller.
Also block the path at your reverse proxy as a second layer:
# nginx in front of Roller
location /roller-services/xmlrpc {
    return 403;
}
Check whether you were hit
grep -i "roller-services/xmlrpc" /var/log/nginx/access.log* /path/to/tomcat/logs/localhost_access_log*Unexpected POST requests to that endpoint, new files in the webapp directory, or unknown child processes of the Java process are signs of compromise. If you find any, rebuild the server rather than just patching it.